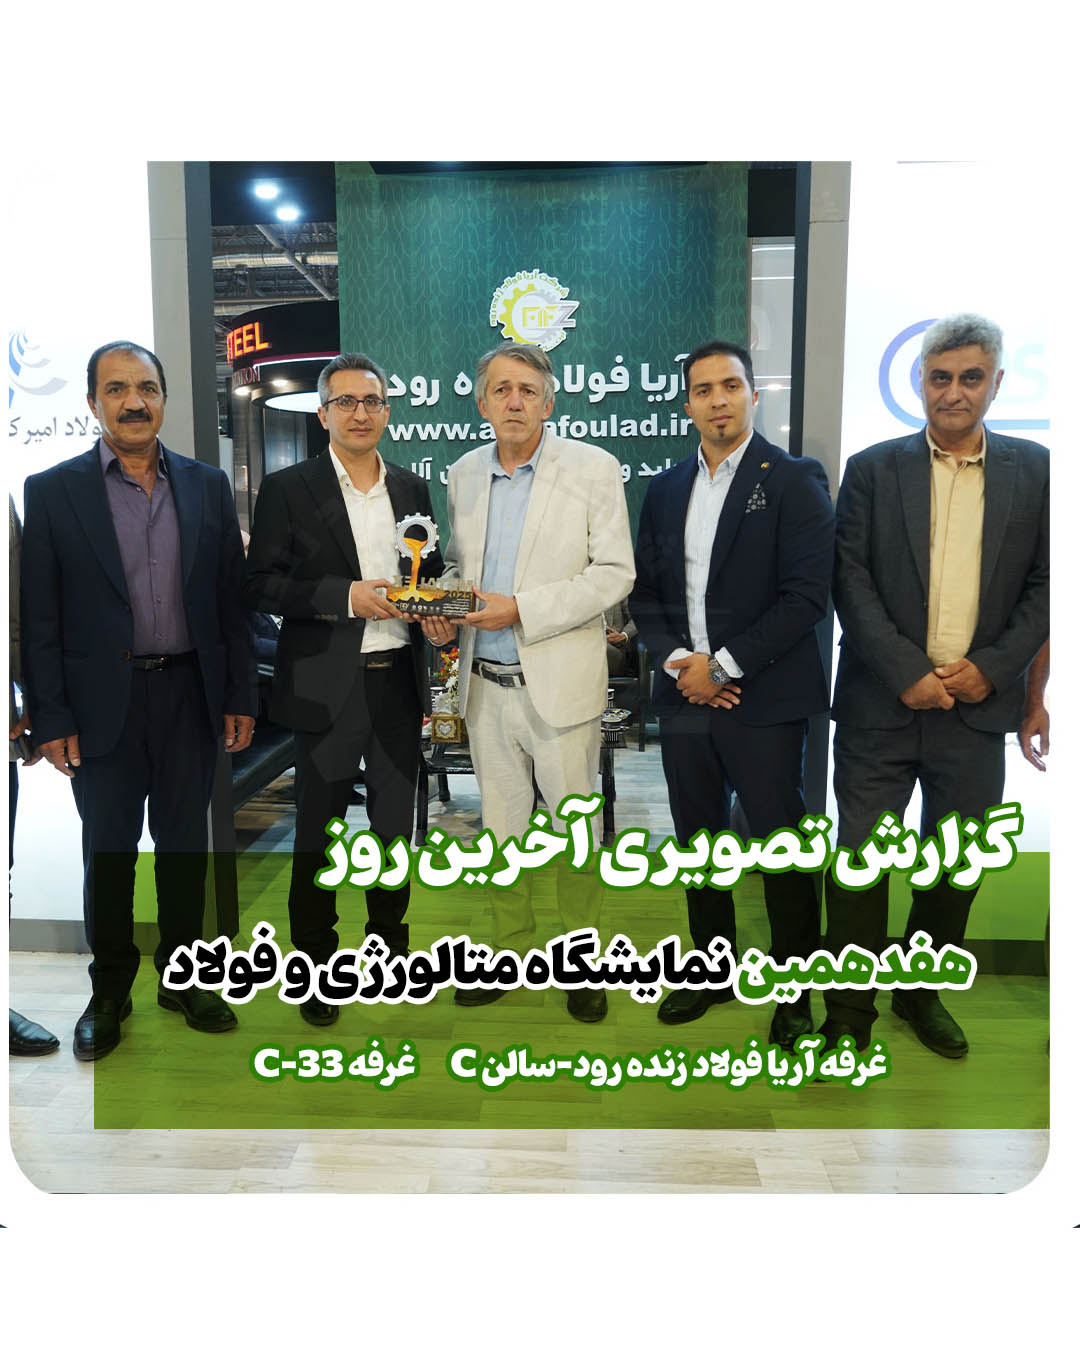
نمایشگاه حضور آریا فولاد زنده رود در نمایشگاه متافو اصفهان شرکت آریا فولاد زنده با هدف معرفی توانمندیها، محصولات و دستاوردهای فنی خود، در نمایشگاه تخصصی متالورژی اصفهان حضور یافت. این نمایشگاه از تاریخ ۱۲ تا ۱۵ شهریورماه برگزار شد و جمعی از فعالان، متخصصان و مدیران صنعت فولاد و متالورژی کشور در آن شرکت کردند. آریا فولاد زنده در طول برگزاری این رویداد، ضمن ارائه آخرین محصولات و خدمات خود در حوزه فولاد، فرصت مناسبی برای تعامل مستقیم با مشتریان، فعالان صنعتی و صاحبان صنایع فراهم کرد. کارشناسان این شرکت با حضور در غرفه، به معرفی ظرفیتهای تولید، فناوریهای بهکاررفته و برنامههای توسعهای شرکت پرداختند. حضور در نمایشگاه متالورژی اصفهان گامی مؤثر در راستای تقویت ارتباط با بازار، تبادل دانش فنی و شناسایی فرصتهای همکاری جدید برای شرکت آریا فولاد زنده بهشمار میرود. این شرکت با تکیه بر کیفیت، نوآوری و تجربه، همواره در مسیر ارتقای جایگاه خود در صنعت فولاد کشور گام برمیدارد. مطالعه
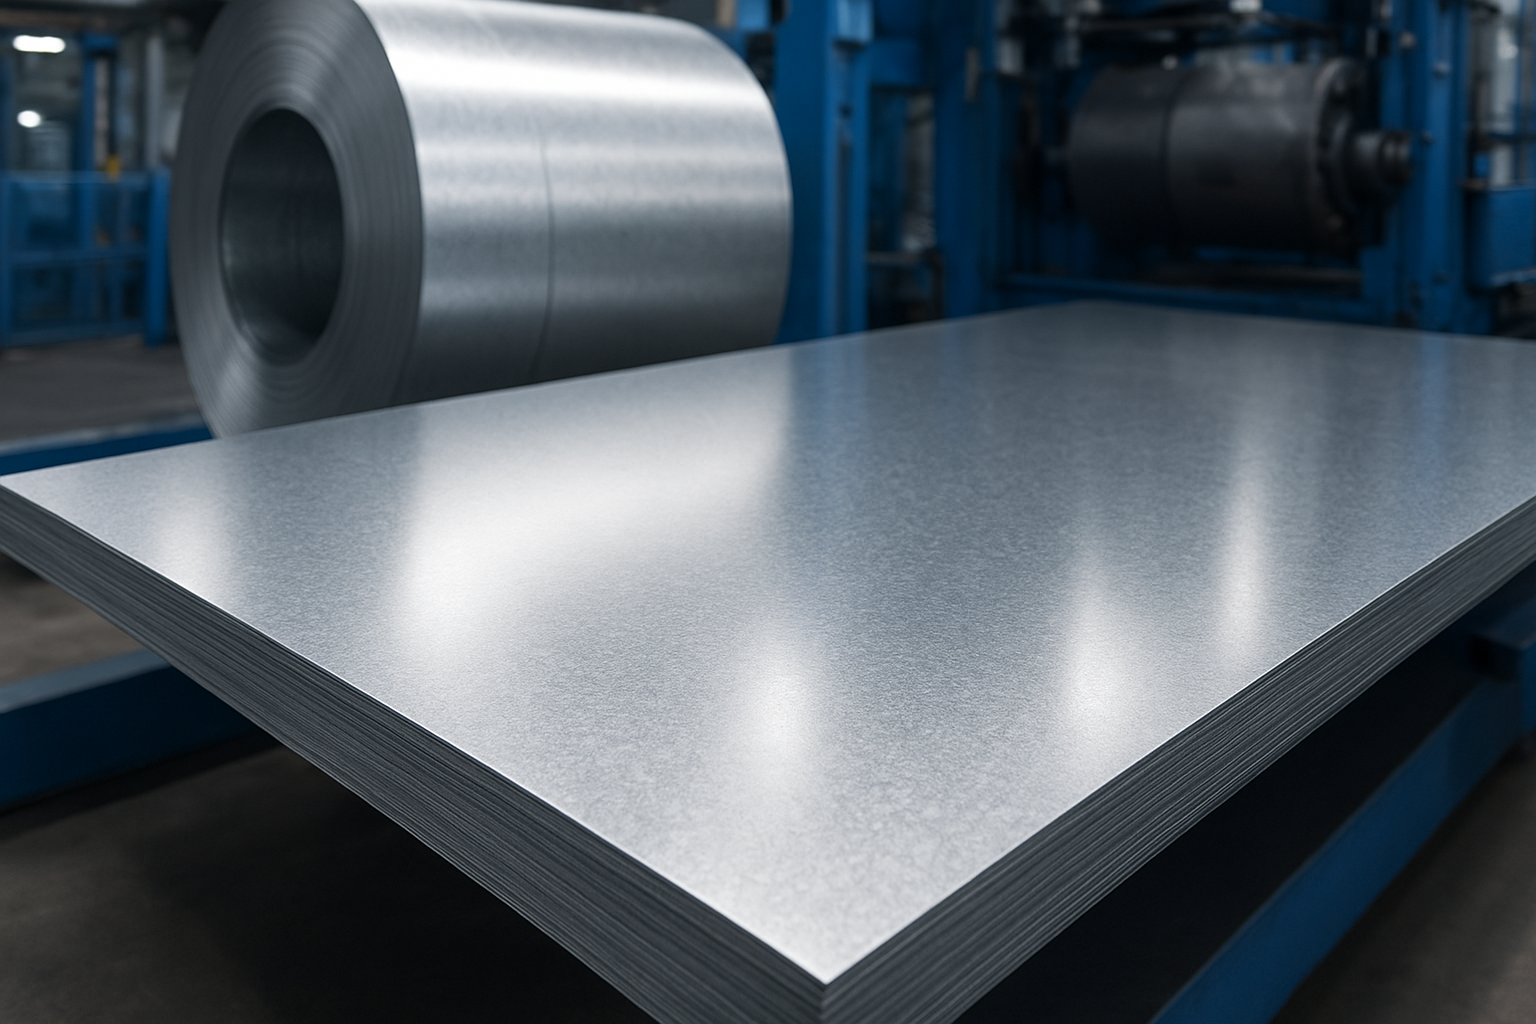
مقالات فولادی بررسی کیفیت و ضخامتهای ورق گالوانیزه ورق گالوانیزه یکی از پرکاربردترین محصولات فولادی در صنایع مختلف بهشمار میرود که بهدلیل مقاومت بالا در برابر خوردگی، طول عمر مناسب و ظاهر یکنواخت، جایگاه ویژهای در بازار دارد. کیفیت این نوع ورق به عوامل متعددی از جمله ضخامت، نوع پوشش روی و فرآیند تولید وابسته است. اهمیت کیفیت در ورقهای گالوانیزه کیفیت ورق گالوانیزه مستقیماً بر دوام و عملکرد آن در شرایط محیطی مختلف تأثیر میگذارد. پوشش یکنواخت روی (Zn) باعث جلوگیری از زنگزدگی فولاد پایه شده و از آن در برابر رطوبت، مواد شیمیایی و عوامل خورنده محافظت میکند. هرچه کیفیت پوشش بالاتر و کنترل فرآیند گالوانیزاسیون دقیقتر باشد، ورق عملکرد بهتری در طول زمان خواهد داشت. از مهمترین شاخصهای کیفیت ورق گالوانیزه میتوان به موارد زیر اشاره کرد: یکنواختی و پیوستگی پوشش روی چسبندگی مناسب پوشش به ورق پایه سطح صاف و بدون موج، ترک یا لکه رعایت استانداردهای بینالمللی و ملی نقش ضخامت در کیفیت و کاربرد ضخامت ورق گالوانیزه یکی از عوامل کلیدی در انتخاب آن برای کاربردهای مختلف است. این ورقها معمولاً در ضخامتهای متنوعی تولید میشوند که هر کدام کاربرد خاص خود را دارند. ضخامتهای پایینتر معمولاً برای مصارف سبک مانند: تولید لوازم خانگی قطعات خودرو کانالهای تهویه بهکار میروند، در حالی که ضخامتهای بالاتر مناسب استفاده در: صنایع ساختمانی سولهسازی سازههای فلزی پوشش سقف و دیوارهای صنعتی هستند. انتخاب ضخامت مناسب نهتنها موجب افزایش استحکام سازه میشود، بلکه از نظر اقتصادی نیز اهمیت زیادی دارد. ارتباط ضخامت با میزان پوشش روی در ورقهای گالوانیزه، علاوه بر ضخامت ورق پایه، میزان پوشش روی نیز اهمیت دارد. پوشش روی معمولاً بر حسب گرم بر متر مربع اندازهگیری میشود و هرچه این مقدار بیشتر باشد، مقاومت ورق در برابر خوردگی افزایش مییابد. ترکیب ضخامت مناسب ورق با پوشش استاندارد روی، کیفیت نهایی محصول را تضمین میکند. جمعبندی کیفیت و ضخامت ورقهای گالوانیزه دو عامل تعیینکننده در عملکرد و طول عمر این محصول هستند. انتخاب ورق گالوانیزه با ضخامت مناسب و کیفیت بالا، ضمن کاهش هزینههای نگهداری، ایمنی و دوام سازه را افزایش میدهد. به همین دلیل، توجه به مشخصات فنی و استانداردهای تولید در هنگام خرید ورق گالوانیزه امری ضروری است. مطالعه
دستهبندی نشده Understanding Cake Wallet’s Open Source Security Audits: What Third Parties Have Verified Security audits are the operational backbone of trust in open-source wallet software. Unlike closed-source systems where security claims rest largely on corporate reputation and legal disclaimers, an open-source wallet can be examined, reviewed, and verified by independent third parties. Cake Wallet, launched in 2018 and now trusted by over one million users, publishes its codebase and has undergone formal security assessments. The question facing potential users is not whether an audit exists, but what it actually examined, what it found, what remains unaudited, and how the findings were addressed. The appeal of an open-source wallet is straightforward: the code can theoretically be read, analyzed, and tested by anyone with the technical capability. In practice, most users rely on summaries, GitHub repositories, and third-party assessments rather than auditing the entire codebase themselves. This creates a secondary trust problem: understanding what an audit covers, how thorough it was, where gaps remain, and whether the findings were material enough to warrant concern or were addressed satisfactorily. Cake Wallet's public commitment to transparency deserves serious evaluation against what that transparency actually reveals. The mechanics of security audits in wallet software A security audit of wallet software typically examines several distinct layers. The first is code logic: does the application implement the intended cryptographic operations correctly? This involves reviewing how private keys are generated, stored, accessed, and used to sign transactions. The second layer is data handling: what information the wallet collects, how it is transmitted, where it is stored, and whether it is exposed unnecessarily. The third is integration: how the wallet communicates with blockchain networks, market makers, routing systems, and hardware devices. Each layer can contain risks that do not appear in the others. Formal security audits typically follow a scope document that specifies which code, features, and dependencies will be examined. An audit of Cake Wallet's core transaction signing logic might not cover every network it supports, every privacy feature, or every version of its dependencies. The audit firm will test against a specified version of the code, meaning that subsequent updates may introduce new issues or fix existing ones without re-audit. This is why the date of an audit matters as much as its findings. A thorough assessment from 2021 may not reflect the current state of the codebase in 2024. The audit process typically involves both static code analysis, where reviewers read and reason about the code without executing it, and dynamic testing, where the wallet is run, monitored, and tested with specific inputs to observe its behavior. Automated tools can flag common patterns such as hardcoded secrets, unsafe cryptographic operations, or missing input validation. Experienced security engineers then examine the findings, assess context, and determine which issues represent genuine risks versus theoretical concerns in limited scenarios. A critical distinction is between a security audit and a full compliance review. An audit focuses on whether the code works as intended and avoids obvious mistakes. Compliance might examine regulatory obligations, user data handling policies, or anti-money-laundering requirements—areas that depend on jurisdiction and business practices rather than technical implementation. Cake Wallet emphasizes privacy and open-source design, but those principles do not automatically satisfy legal or compliance questions in every jurisdiction where it is used. Publicly disclosed audit findings and their scope Cake Wallet's development team has maintained a presence in security-conscious communities and has engaged with auditors willing to assess the codebase. The specifics of published audits depend on what the team has chosen to disclose. Many companies perform audits but do not publish full reports, citing competitive concerns or preferring to address findings privately before public disclosure. Cake Wallet's approach is more transparent than that of many closed-source wallet providers, but users should verify what is actually available versus what is claimed. The structure of disclosed findings typically follows a severity classification: critical vulnerabilities that could directly compromise funds, high-severity issues that could weaken security under specific conditions, medium issues that represent design concerns or edge cases, and low-severity items that are mostly informational. A report might find zero critical issues while identifying several medium and low findings. This is a reasonable and common result; the presence of findings does not invalidate the entire wallet, but rather indicates areas where the team should respond. When evaluating audit reports, specific technical findings matter more than summary conclusions. A report stating "the wallet does not have critical vulnerabilities" is less informative than one that specifies: "the wallet correctly implements BIP39 key derivation on iOS, though the Android version was not audited." That level of detail allows users to understand what was verified, what was not, and what assumptions the audit made. Likewise, a finding such as "the wallet collects minimal on-device data" is more useful when paired with evidence about which specific data fields are retained and which are discarded. Open-source projects benefit from continuous auditing by researchers who publish findings in academic papers, security conferences, or vulnerability databases. If independent researchers have examined Cake Wallet and published their work, that constitutes a form of public verification. Users can check GitHub issues, commit histories, and security advisory databases for references to discovered and patched vulnerabilities. The existence of patched issues demonstrates that the team responds to problems, while the absence of issues across many years would be suspicious rather than reassuring. What a third-party audit cannot guarantee An important reality is that a security audit, no matter how thorough, provides a snapshot of the code at a specific time. If Cake Wallet pushes a new update the day after an audit is completed, that update is unaudited. This does not mean the update introduces vulnerabilities, but it does mean the assurance provided by the audit no longer covers the latest version. Users who update frequently or automatically may be running code that has not been formally reviewed. This is an inherent limitation of rapid-iteration software development, not a flaw unique to Cake Wallet. Audits also typically do not cover the entire dependency tree. Cake Wallet, like any modern application, relies on libraries for cryptography, networking, user interface, and other functions. An audit of Cake Wallet's code might not examine every version of every dependency, and vulnerabilities discovered in those dependencies after the audit may not be immediately visible without additional investigation. The team's process for updating dependencies, monitoring security advisories, and testing compatibility becomes as important as the audit result itself. The operating system and hardware on which the wallet runs also matter. A wallet that handles private keys correctly may still be compromised by malware at the device level, a modified operating system, or a physical attack on the device itself. An audit cannot verify the security of the Android or iOS ecosystem; it can only assess whether the wallet makes reasonable assumptions about what those platforms provide. If a user runs Cake Wallet on a device already compromised by a trojan, the audit provides no protection whatsoever. Finally, audits typically do not assess user behavior or social engineering risk. A wallet that correctly implements every feature can still be misused. A recovery phrase written in a notebook left on a desk, a password reused across multiple services, or a user who approves a transaction without verifying the destination are behavioral risks that no technical audit can eliminate. The best-audited wallet in the world cannot prevent a user from voluntarily disclosing their secret key. Hardware integration and network connectivity in audited scope Cake Wallet's support for hardware wallets such as Ledger introduces additional complexity in the audit scope. The wallet software communicates with the hardware device but does not control it; the Ledger device handles the actual signing. An audit of Cake Wallet's code might verify that the wallet correctly formats the transaction data sent to the device, but the Ledger firmware itself is audited separately by Ledger. The security of the combined system depends on both components functioning correctly and the communication between them being secure. Network connectivity—including Tor routing, node selection, and communication with blockchain networks—also requires specific audit attention. A wallet might handle private keys perfectly but leak information through network requests. For example, if the wallet requests the balance of a specific address from a node, the node operator can infer that the user controls that address. Cake Wallet's privacy tools and Tor support are designed to mitigate this, but an audit must specifically examine network behavior to verify the protections work as intended. Generic code review may not catch privacy leaks that only appear through network analysis. The exchange functionality built into Cake Wallet—the ability to swap between assets within the wallet interface—adds another auditable surface. The wallet displays quotes from market makers, formats requests, sends transactions, and waits for settlement. An audit should verify that quoted amounts are accurately displayed, that no value is diverted, and that the user can verify the destination address before approving. If the audit was conducted before exchange features were added, users cannot assume that feature has been verified. Biometric login and 2FA functionality must also be assessed in context. The audit should verify that the wallet does not store the actual secret key in a way that can be bypassed by defeating the biometric or 2FA mechanism. Some implementations place private keys in a protected enclave and never expose them outside that boundary; others may have weaker separation that allows alternate authentication to grant key access. The specific mechanism matters significantly. How the open-source model enables ongoing verification The primary advantage of open-source design is that Cake Wallet's code can be examined by independent researchers, competing wallet vendors, security-focused developers, and community members. This creates multiple layers of potential verification that extend far beyond any single audit report. If a vulnerability exists in the codebase, there is a theoretical pathway for it to be discovered by someone other than the development team, reported responsibly, and fixed before exploitation. GitHub's public repository structure allows users to review the commit history, compare versions, and understand what changed between releases. A user concerned about a specific feature can examine the code directly or read the discussion in pull requests and issues. This transparency does not make every user a security expert, but it enables technically capable users to verify claims and identify problems. It also creates accountability: if the team makes a claim about privacy or security, the code is publicly available to prove or disprove it. The continuous-audit model enabled by open source also benefits from the phenomenon of "many eyes." Security researchers, academic institutions, and independent auditors can examine the code without requiring an explicit engagement from Cake Wallet. Publications in security journals, presentations at conferences, and vulnerability reports submitted through responsible disclosure channels all contribute to the overall assurance. A wallet that has been examined this way across multiple years and versions has stronger evidence of security than one audited once at a specific point in time. However, open source is not a guarantee of security. The code being publicly available does not mean it has actually been audited. A feature that appears insecure in the repository might be insecure because no one with sufficient expertise has examined it carefully. Conversely, users should be cautious of the opposite assumption: that a feature is secure simply because the code is visible. The security value of open source depends on whether capable reviewers actually engage with the code and whether they have incentives and mechanisms to report findings. Trusting the team behind audited code The credibility of an open-source wallet depends partly on the team that maintains it. Cake Wallet's development history, contributors, and responsiveness to security reports all contribute to the case for trust. A team that patches vulnerabilities promptly, communicates clearly about changes, and maintains backward compatibility with older versions (when practical) demonstrates commitment to user security. A team that ignores bug reports, delays patching known issues, or makes cryptographic changes without explanation raises justifiable concerns. The team's resources also matter. A well-funded project can engage professional auditors regularly, whereas a volunteer-driven project may rely on community review and academic researchers. Neither situation guarantees security, but they have different risk profiles. Cake Wallet, as an established wallet with over one million users, has the resources to engage auditors and maintain professional development practices. Users can verify this by examining hiring announcements, job postings, and the pace of development and maintenance. The alignment between the team's claimed priorities and their actual practices also warrants examination. If Cake Wallet claims to prioritize user privacy but runs code that connects directly to nodes without Tor routing, that is a discrepancy worth understanding. If the team emphasizes open-source review but removes comments from the code or obfuscates key sections, that is another red flag. Users can download the wallet yourself and review it—or look for published reviews from others who have done so—available here. Finally, the team's approach to disclosure of found vulnerabilities indicates maturity. A responsible team will have a process for receiving security reports, assessing them, fixing issues, and issuing updates before publicly announcing the vulnerability. This gives users time to update before attackers can exploit the issue. A team that ignores private security reports or disputes findings publicly, rather than investigating and fixing, demonstrates poor security discipline. Comparing audit findings across wallet implementations Users evaluating wallet security often benefit from comparing how different implementations handle the same problem. If multiple wallets have been audited for key derivation, address generation, or transaction signing, the audit reports can provide evidence of which approaches are more secure. Cake Wallet's implementation can be assessed against Bitcoin Core's, Monero's reference wallet, or other established projects. This comparative approach reveals not whether Cake Wallet is perfect, but whether its design choices are sound relative to alternatives. Such comparison also highlights where Cake Wallet's scope differs from other wallets. A wallet that supports five networks must implement five separate integrations, each potentially requiring specific security considerations. A single-network wallet can focus more deeply on that one implementation. The breadth of asset support in Cake Wallet—Monero, Bitcoin, Ethereum, Litecoin, and others—means a comprehensive audit would need to cover all of those integrations. If an audit was limited to Bitcoin support, users cannot assume Monero handling was equally verified. The audit landscape has also evolved. Older audits used different methodologies and standards than current practice. A wallet audited in 2018 with state-of-the-art techniques of that time might not meet the standards of a 2024 audit. This does not mean the wallet became less secure, but rather that the criteria for evaluation have advanced. Users should consider both the absolute findings and the freshness of the assessment when evaluating wallet security. Practical steps for users assessing Cake Wallet's security posture A user seeking to evaluate Cake Wallet's security can take several concrete steps. First, locate any published audit reports from the team's website, GitHub repository, or announcements. Read the full report, not just the executive summary, and note the scope, version audited, date, and specific findings. Second, search for security advisories related to Cake Wallet in databases such as CVE, GitHub Security Advisories, or security researcher publications. Third, examine the GitHub repository's commit history, issue tracker, and pull requests to understand how the team responds to potential problems. Fourth, if you have technical capability, download the source code and review it yourself, or have a trusted developer review it. This is the ultimate verification possible with open-source software. Fifth, look for community discussions, security analyses, and third-party reviews published by security researchers or journalists. If a wallet has a known vulnerability, it is likely to be discussed in security forums or documented in research. Sixth, evaluate the team's current development practices: are they updating dependencies regularly, responding to security reports, and maintaining backward compatibility with older versions when appropriate? Seventh, understand what the wallet claims to do and what it does not claim. If the audit report verified the wallet's key derivation but did not cover its exchange functionality, do not assume exchange operations were audited. Read the scope carefully. Eighth, test the wallet with a small amount before trusting it with significant funds. Confirm that you can create a wallet, generate an address, receive a test transaction, send a test transaction, and recover the wallet using a backup seed phrase. This operational testing will reveal problems that a code audit might miss. Finally, maintain realistic expectations about what an audit can guarantee. A positive audit report indicates that third parties have examined the code and found no critical flaws at that point in time. It does not guarantee that future versions will be equally secure, that behavioral risks are eliminated, or that the wallet cannot be misused. Security is not a one-time certification; it is an ongoing practice of careful software development, timely patching, and user awareness. Frequently asked questions Has Cake Wallet undergone professional security audits? Yes, Cake Wallet has been reviewed by third-party security auditors. The team publishes information about these assessments on their public channels. Users should locate the specific audit reports, review their scope and findings, and note the version and date of the audit to understand what has been verified and what may have changed since the assessment was conducted. What does an open-source audit guarantee about Cake Wallet's security? An open-source audit verifies that the code does not contain obvious cryptographic flaws, logical errors, or unsafe data handling at the time it was audited. It does not guarantee that the wallet cannot be misused, that subsequent updates are equally secure, that all networks and features have been equally reviewed, or that operational risks such as device compromise are prevented. Open source enables ongoing verification, but does not replace user responsibility. If an audit found issues, does that mean Cake Wallet is unsafe? No. Security audits routinely identify findings ranging from critical to informational. The important questions are: how severe were the findings, have they been fixed, and how did the team respond? A wallet that identifies and fixes issues demonstrates good security practices. A wallet that ignores findings or hides them is more concerning than one that discloses and addresses them promptly. مطالعه
دستهبندی نشده How I Hunt Fragile Liquidity Pools: A Practical Guide from the DEX Frontlines Whoa! I stumbled into a strange liquidity pool last week. It smelled like yield farming but there was a catch. My first gut reaction was excitement followed by instant skepticism. Initially I thought the impermanent loss would obliterate any gains, but after tracing token flows and on-chain swaps across pairs for hours I realized the real risk was concentrated slippage due to a handful of large LPs that dominated the pool. Seriously? The pool's TVL looked healthy on surface metrics though. Traders had volume spikes that were hard to ignore. But when I pulled the tick-level data and watched the dex swap trails in real time with a proper analyzer, patterns emerged showing wash trading and recycling of tokens between shadow wallets that artificially inflated volume metrics and hid liquidity concentration. On one hand the APY projections flashed green alluringly; on the other hand the order book depth evaporated when price deviated by a few percent because market makers were thin or absent, which made me uncomfortable. Hmm... Here's the thing, metrics lie without context and narratives can be engineered. I checked LP token distributions across wallets and timestamps. The top five holders controlled over half the liquidity. That concentration meant a handful of wallets could withdraw or rebalance and swing the pool price violently, which undermines the primitive assumption many analytics dashboards use when signaling 'safe' pools to retail traders. Wow! Liquidity math looks simple on paper for most folks. But the composability of tokenomics complicates risk models dramatically. I dug into token vesting schedules, found cliff releases and smart contract admin keys that were active, and then mapped how those events coincided with sudden LP adjustments that preceded price dumps, which felt like detective work. Actually, wait—let me rephrase that: this isn't just detective work, it's pattern recognition across time-series, on-chain intents, governance moves, and off-chain narratives that all influence usable liquidity and the apparent robustness of a pool. Okay, so check this out— You need multiple lenses to assess a pool's safety. Wallet clustering, slippage simulation, and depth analysis are non-negotiable. Volume alone is a very very important but misleading signal. (oh, and by the way... I sometimes backtest small trades on mainnet fork sandboxes to validate behavior) I run synthetic trades against the pool parameters to see realized slippage at different trade sizes, and that operational test often reveals fragility that aggregate metrics like TVL and 24h volume simply cannot. I'm biased, but... Analytics tools matter a lot for real-time decisions in fast markets. I used a dashboard and then cross-checked on-chain events manually. Check this: I once watched a pool that showed steady volume while a token pair was being resupplied from an exchange arbitrage bot, and only by correlating mempool activity with swap receipts could I tell the direction and likely short-term stability of the liquidity. If you rely solely on flashy charts without the ability to follow token trails and wallet histories, you're essentially trading blind into crowded and often-manipulated markets. Something felt off about... For retail traders, that blind spot is dangerous especially when leverage is available. I've seen people lose savings because of naive pool picks. Here's what bugs me about many dashboards though they favor surface-level signals. They aggregate disparate signals into a single risk score without exposing the mechanics behind that score—so users can't tell whether a 'low risk' label stems from genuine diversified liquidity or just aggressive obfuscation. I'm not 100% sure, but... A small governance vote can flip perceived safety overnight. Watch vesting calendars and multisig changes closely as if your capital depends on it. I map contract calls, check admin keys, and then simulate stress trades to see whether liquidity providers are aligned with long-term token holders or short-term extractors, and that layering often separates resilient pools from the ones that fail within a week. On the one hand you have protocols with transparent incentive alignment and multi-sig governance; on the other hand you find emergent schemes that look the same superficially yet hide single points of failure that show up under panic. Tool in my belt I use dexscreener when I want quick market context and pair-level depth, alerts, and live swaps that help me prioritize which pools to stress-test next because speed often matters more than perfect data in these windows. Really? Tools like order book replicas help with intuition for illiquid tokens. Now combine that with wallet flow visualization and you get actionable signals. I check pair-level depth to gauge slippage risk before sizing trades. That toolset—combined with manual forensics—lets me act when edges are exposed rather than when headlines signal opportunity. I'll be honest... Education beats hype every time in these markets especially for new entrants. Start small, simulate, and never ignore admin keys or looming vesting events. I'm sketchy on some governance rumors and can't vouch for every protocol, but my workflow—cluster wallets, simulate slippage, check multisig, tie volume to real swaps—has consistently reduced surprises for trades I've executed and for clients I've advised. So, if you want a practical playbook: instrument pools with stress tests, watch wallet concentration, triangulate volume, and keep an eye on governance; do those things and you'll avoid many common traps that make 'high yield' a fast way to burn capital. FAQ How do I start testing a pool without risking much capital? Begin with tiny synthetic trades in a forked environment or use minimal on-chain settlements sized to the slippage you can tolerate; combine that with checking LP concentration, recent vesting events, and multisig changes—if those checks flag risk, walk away or reduce exposure. Somethin' as small as a $50 test swap can tell you more than a dozen charts; it's a cheap, practical habit that protects capital. مطالعه
دستهبندی نشده Using Ledger Wallet Offline Mode: Transaction Preparation Without Internet Connection A cryptocurrency holder with significant assets faces a practical security dilemma: maintaining active portfolio monitoring while minimizing exposure of private keys to any internet-connected device. The standard software wallet approach—storing keys on a phone or desktop—accepts network connectivity as a given security cost. Hardware wallets like Ledger solve part of that problem by keeping keys isolated in a Secure Element, but the companion application still requires internet access to fetch balances, broadcast transactions, and display network activity. An offline transaction preparation workflow removes that requirement entirely: the user can construct and review unsigned transactions on a disconnected machine, then transfer them to a connected device only for signing and broadcasting. This approach is not common, nor is it marketed as a primary feature of Ledger Wallet. Most users rely on the standard connected workflow where the application fetches blockchain data in real time. However, the underlying architecture supports offline preparation because Ledger Wallet does not store or process private keys; it only constructs transaction objects that must be signed by the hardware device. Understanding how to execute this workflow requires attention to data formats, address synchronization, and the precise steps needed to move unsigned transactions between machines while maintaining security integrity. Why offline transaction preparation matters for high-security deployments The security model of a hardware wallet like Ledger depends on isolation: private keys remain in the Secure Element, never exposed to the host computer's operating system or application memory. That isolation is effective only if the host machine itself is trustworthy. A compromise at the OS level, a keylogger, or malware with sufficient privileges can still observe transaction details, addresses, and amounts even though it cannot steal keys. For users managing large balances or working in high-threat environments, accepting any network connection on the transaction-construction machine introduces unnecessary risk. Offline preparation splits the workflow into two separate security domains. The offline machine constructs the transaction based on local data: the user's own address list, cached blockchain information, and the target recipient. The connected machine only performs the final signing step, which requires the Ledger device itself. If the offline machine is compromised, the attacker sees transaction data but cannot access private keys and cannot modify the transaction after the user moves it to the signing machine. If the signing machine is compromised, an attacker cannot change the transaction contents because the unsigned object is already fixed before it arrives. This is most useful in scenarios where one of the two machines can be more trustworthy than the other. A user might maintain an isolated offline desktop for transaction preparation and use a separate, regularly connected laptop only for final signing and broadcast. Alternatively, a business operating a multisig vault might use one air-gapped machine for preparing transactions and a different connected setup for coordinating signatures among multiple signers. The specific setup depends on the threat model, but the principle is consistent: separate the machines that hold data from the machines that hold keys. Understanding Ledger Wallet's architecture and data requirements Ledger Wallet operates as a user-facing application that connects to the Ledger device via USB or Bluetooth and to the blockchain via public nodes or Ledger's infrastructure. The application maintains a local database of accounts, addresses, and transaction history. When preparing a transaction, Ledger Wallet constructs an unsigned transaction object that includes the sender's address, recipient, amount, estimated fees, and other network-specific parameters. This object is not signed until it reaches the hardware device, which means it can be reviewed, saved, and transferred without compromising key material. The critical technical requirement for offline operation is that the offline machine must have access to the same account data—specifically, the list of derived addresses for each account. Ledger Wallet generates addresses deterministically from the recovery phrase, but since the recovery phrase never leaves the hardware device, the offline machine cannot generate new addresses on its own. Instead, it must work with addresses that were already derived and cached during a previous connected session. This is why the offline workflow is not a one-time operation: it assumes that the user has previously connected the device, allowed Ledger Wallet to synchronize account information, and cached that data on the offline machine. For Bitcoin, Ethereum, and other supported networks, the synchronization process fetches the receiving and change addresses for each account and stores them locally. Once cached, these addresses can be used to construct transactions without any further network access. The offline machine can then display balances based on previous data, estimate fees using locally stored information, and create the unsigned transaction. None of this requires internet connectivity because none of it involves key material—only addresses and transaction structure. Setting up an offline machine for transaction preparation The practical starting point is to download and install Ledger Wallet on both the offline and connected machines. Users should obtain the software from the official Ledger website to ensure authenticity, as the application is free to download and updates are critical for security. After installation on the offline machine, the user should connect the Ledger device temporarily to allow Ledger Wallet to fetch and cache account information. This synchronization step is essential: the offline machine must know which addresses belong to the user before it can construct transactions. During this synchronization, Ledger Wallet will request permission to access the device, display account balances, and store address data locally. The user should allow this and let the application complete its initial scan of all accounts. Once synchronization is finished, the device can be disconnected and the offline machine can be powered down or taken offline permanently. The cached address information remains on the disk, allowing future transaction preparation without further device connection. Important configuration considerations include enabling address verification on the hardware device if high security is required. When the user constructs a transaction specifying a recipient address, Ledger Wallet can optionally display that address on the device screen during signing, allowing the user to confirm that the address shown in the application matches what the device will actually sign. This prevents a compromised offline machine from silently changing the recipient. The user should also consider whether to enable fee confirmation on the device, which adds an extra verification step. For the offline machine itself, the security posture depends on the deployment model. An air-gapped machine that never connects to any network and is physically isolated from shared devices offers maximum protection. A machine that occasionally goes online for other purposes introduces more risk; if it is compromised by malware, that malware could potentially modify transactions or addresses stored on it. The safest approach is a dedicated machine used only for offline transaction preparation, never for browsing, email, or other network activity. Preparing unsigned transactions on the offline machine Once the offline machine has cached account data, preparing a transaction follows a familiar workflow within Ledger Wallet. The user navigates to the desired account, selects "Send," specifies the recipient address, enters the amount, and reviews the proposed transaction. At this stage, the offline machine displays estimated fees based on locally stored fee data—not current network rates, since it has no network access. This is a limitation that the user must accept: the fee estimate may be outdated by hours or days if market conditions have changed significantly. The unsigned transaction object can be exported or saved in a format suitable for transfer to the connected machine. Depending on the Ledger Wallet version and network, this might be a file, a QR code, or other serialized format. The exact method varies by platform and update status, so users should consult the application's documentation or recent release notes for the specific export mechanism. The key requirement is that the transaction must remain unsigned and in a format that the connected machine can recognize and import. Before exporting, the user should verify all transaction details on the offline machine's screen: the recipient address, the amount, the fee, and the sending account. This verification is important because the offline machine is where the user exercises direct control over the transaction contents. Any error confirmed at this stage will be difficult to correct later. The user should also verify that the recipient address is correct by comparing it to an independent source—not just copied from an email or chat, which could have been intercepted or altered. The unsigned transaction file or data must then be transferred to the connected machine. This transfer can occur via USB drive, external storage, or other offline media. The user should not email the transaction, use cloud storage, or transfer it over a network connection, as these introduce exposure and potential interception. A physical USB drive is the most straightforward approach: the offline machine writes the unsigned transaction to the drive, the user physically carries the drive to the connected machine, and that machine reads and imports the transaction. Signing and broadcasting from the connected machine Once the unsigned transaction reaches the connected machine, Ledger Wallet on that device can import and prepare it for signing. The connected machine must have the same Ledger Wallet installation and be connected to the same Ledger device. When the user imports the unsigned transaction, the application displays the transaction details again, providing a second opportunity for verification. At this point, the user should again confirm the recipient, amount, and fee—even though these were already verified on the offline machine—because this is the final moment before the private key is involved. After verification, the user initiates the signing process. The unsigned transaction is passed to the Ledger device via USB or Bluetooth, and the device displays the transaction details on its screen. The user confirms the transaction on the device itself, which performs the signing operation within the Secure Element. Once signed, the transaction object is returned to Ledger Wallet on the connected machine. At this point, the transaction is complete and ready to broadcast to the network. Broadcasting occurs immediately or on the user's command, depending on settings. The connected machine submits the signed transaction to the blockchain through public nodes or Ledger's infrastructure. The transaction then enters the network's mempool and begins confirmation processing. From this point forward, the transaction follows the normal consensus rules of the network; there is no further role for Ledger Wallet or the device. The signed transaction can be verified on any block explorer using its transaction hash. The user should record this hash and verify confirmation over the following minutes or hours, depending on network congestion. If the transaction does not appear within a reasonable time, it may have been rejected due to insufficient fees, double-spending, or other validation failures. In that case, the user would need to construct a new transaction with adjusted parameters on the offline machine and repeat the process. Addressing practical limitations and error recovery The offline transaction preparation workflow is more secure than a fully connected setup, but it introduces operational friction that users must tolerate. Fee estimation is the most obvious limitation: without current network data, Ledger Wallet on the offline machine cannot know whether the estimated fee is appropriate for current conditions. If fees have risen sharply, the offline estimate may be far too low, causing the transaction to be rejected or delayed indefinitely. Conversely, if fees have fallen, the user may overpay by using an outdated estimate. Mitigating this requires either accepting potential overpayment or periodically updating the offline machine's fee data. Some users refresh fee information by connecting the offline machine to the internet once per day or week, allowing Ledger Wallet to synchronize network conditions and then disconnecting again. This reduces but does not eliminate the staleness problem. Others accept higher fees as the cost of offline operation, particularly if the transaction amount is large relative to the fee itself. Address validation is another consideration. If the offline machine is compromised, an attacker could theoretically modify the recipient address before the user exports the transaction. The user would then sign a transaction to the wrong address on the connected machine, and the funds would be lost. Mitigating this requires verifying the recipient address through an independent channel—for example, by having the recipient confirm the address verbally, in person, or through a separately secured communication channel. This is a best practice regardless of whether the offline machine is used, but it becomes more critical when the offline machine is part of the security model. Recovery from a failed transaction is straightforward: the user constructs a new transaction on the offline machine with adjusted parameters and repeats the signing and broadcast steps. If the original transaction was never confirmed, it will eventually be dropped from the network's mempool and the funds will remain unspent. If it was confirmed, the user must wait for the output to become spendable in a new transaction. For Bitcoin and similar systems, this depends on the confirmation count; for Ethereum and account-based systems, the process is different but similarly deterministic. Hardware device security and recovery phrase protection The offline transaction preparation workflow does not change the fundamental security of the Ledger device or recovery phrase. Private keys remain in the Secure Element, protected by the device's firmware and cryptographic design. The recovery phrase should be protected with the same care regardless of whether transactions are prepared offline or online: never exposed to any internet-connected device, stored securely offline, and tested only under controlled conditions. If the recovery phrase is compromised, the attacker can access funds regardless of how carefully transactions are prepared or signed. The offline machine and connected machine are both irrelevant in that scenario. Therefore, private key protection at the recovery phrase level is the foundation of security. The offline workflow addresses a different threat: the security of the transaction construction and signing process itself, not the security of the key material. Users should also ensure that both machines—the offline and connected—receive timely security updates for the operating system and Ledger Wallet itself. The offline machine should be updated while it is still connected to a network, then disconnected permanently or used only for transaction preparation with no other network activity. The connected machine should maintain regular updates to protect against malware and network attacks. If either machine shows signs of compromise (unusual behavior, unexpected network activity, missing files), the user should assume that security may have been breached and take appropriate remedial action, which may include recovering funds from the device to a fresh address on a new device. Comparing offline preparation to standard connected workflows The standard Ledger Wallet experience—connected to the internet, synchronized in real time, signing transactions immediately after creation—is more convenient for most users. The application updates balances automatically, provides current fee estimates, and eliminates the need for manual data transfer between machines. For users who trust their primary machine's security posture and prioritize usability, this is a reasonable choice. Offline transaction preparation suits specific use cases: large balances where the security investment is justified, high-threat environments where the primary machine may be compromised, or organizational settings where transaction preparation and signing are intentionally separated among different people or machines. It also appeals to users who philosophically prefer to minimize their internet-connected device's access to key material, even if the keys themselves are protected by hardware. The trade-off is always between security and convenience. Offline preparation increases security against a compromised connected device at the cost of manual transfers, potentially outdated fee estimates, and additional steps for each transaction. This trade-off is reasonable if the threat model justifies it; it is unnecessary overhead if the primary risk is account takeover or network-level attacks rather than device-level compromise. Getting started with Ledger Wallet and ensuring secure download Before implementing an offline transaction preparation workflow, users must obtain Ledger Wallet from a trustworthy source. The application can be downloaded from the official Ledger website, and users should verify the authenticity of their download by checking file signatures or comparing checksums if available. Obtaining software from unofficial sources, mirrors, or third-party repositories introduces significant risk of malware infection, which would undermine the security of the entire offline workflow. Once obtained, users can review the system requirements for their offline and connected machines. Ledger Wallet runs on Windows, macOS, and Linux, though specific versions and update compatibility may vary. The offline machine should run a supported operating system; using deprecated or unsupported platforms increases security risk. Similarly, the Ledger device itself requires a recent firmware version to support all transaction types and security features. Users interested in implementing this workflow should begin by testing it with a small, non-critical transaction. This allows them to understand the exact steps, identify any compatibility issues, and verify that the export-import process works correctly before attempting to move significant funds. The test transaction should move funds from one account to another within the user's own control, not to an external recipient, so that any errors do not result in permanent loss. Documentation and support are available from Ledger's official channels. Users can consult the Ledger Live download page and related guides to understand the current application capabilities, which may differ from earlier versions. The offline transaction preparation feature is supported, but specific implementation details depend on the network, platform, and application version. Users should not assume that procedures described in older articles or forums remain accurate without verification against the current software. Frequently asked questions Can I prepare a transaction completely offline without ever connecting to the internet? No. The offline machine must initially connect to Ledger Wallet to synchronize account information and cached address data. Once that synchronization is complete, the machine can go offline for transaction preparation. However, the device must eventually be moved to a connected machine for signing and broadcast. At least one machine in the workflow must have internet access at some point. What happens if I use an outdated fee estimate from the offline machine? If network fees have risen significantly, your transaction may be rejected or stuck in the mempool indefinitely. If fees have fallen, you may overpay but the transaction will still be confirmed. The fee is not recoverable after broadcasting, so users should either accept potential overpayment or periodically update the offline machine's fee data by temporarily connecting it to the internet. Does offline transaction preparation protect my private keys better than a standard connected workflow? It protects against compromise of the machine that constructs transactions, but not against compromise of the recovery phrase itself. Private keys remain in the Secure Element regardless of whether the transaction is prepared offline or online. If the recovery phrase is compromised, offline preparation offers no additional protection. The value is in protecting the transaction construction process and the connected machine from exposure during preparation. مطالعه
دستهبندی نشده Why Solana NFTs, Browser Wallets, and Solana Pay Are Suddenly the UX Winners Okay, so check this out—Solana's been quietly eating the lunch of slow chains. Wow! Transaction fees that feel like pennies, instant confirmations, and a flood of NFT projects that actually load fast. My instinct said this would be a short-lived hype. But, initially I thought scalability would bring tradeoffs in UX; then I realized that the wallet layer and payments stack are doing a lot of the heavy lifting. Really? Yes. When NFT marketplaces, browser extension wallets, and Solana Pay line up, you get a user flow that looks like modern e-commerce more than old-school crypto. Hmm... that matters. Because most people don't want to manage raw keys or wait minutes for a transfer. They want to press buy and carry on with their day. Here's the thing. NFT marketplaces on Solana are optimized for speed and low cost. Medium-sized collections and microtransactions work seamlessly. Browser extension wallets act as the local gatekeeper for identity and signatures. Solana Pay, meanwhile, gives merchants a simple protocol for fiat-like experiences. Put them together and you have a near-instant mint-to-checkout path that feels familiar to folks used to web apps. How the pieces fit (and why the wallet matters) Start with the marketplace. It lists NFTs, handles order books or buy-now pricing, and shepherds metadata. Then the browser extension wallet prompts for signature, manages tokens, and holds a UI for NFTs and tokens. Solana Pay plugs in at checkout, translating those on-chain events into merchant-friendly receipts. On one hand it's simple. On the other, the UX and security of that browser wallet determine whether users come back. Phantom-style wallets (light, browser-first) have a clear advantage here. They are built with the Solana UX assumptions in mind: discrete token accounts, fast signature prompts, and minimal friction for NFT metadata display. I'm biased, but for people exploring DeFi and NFTs on Solana, a smooth extension wallet lowers the barrier dramatically. You can check a widely used option here: https://sites.google.com/cryptowalletuk.com/phantom-wallet/ Something felt off about early wallet experiences—permissions dialogs that read like legalese, confusing token accounts, and stray popups. Those are getting cleaner. Though actually, wait—let me rephrase that: they're not perfect yet. Wallet UX has improved, but bad flows still exist (phishing dialogs still work too well). On a practical level, pick a wallet that limits permissions, provides clear signing details, and lets you toggle networks easily. Security matters. Short sentence. The extension is your local private key manager. Don't treat it like a toy. If you're storing high-value assets, use hardware wallets or multi-sig solutions (for projects). For daily NFT browsing and occasional buys, a well-reviewed browser wallet is fine, but keep seed phrases offline and never paste them into a website. Seriously? NFT Marketplaces on Solana — the good, the weird, and the practical Good: instant mints, cheap royalties, and meta-efficient collections that don't bloat the chain. Weird: a marketplace can push an update that breaks metadata links or create comparability issues across wallets. Practical: look for marketplaces that use decentralized metadata standards and provide preview images directly in the listing so your wallet can show a proper thumbnail before you sign anything. On one hand, marketplaces democratize minting and discovery. On the other hand, the speed of Solana markets means you can mis-click just as fast. My gut told me to slow down, and that remains constructive advice—confirm what you're buying, and verify collection contracts when possible. There are wallet features (view contract URL, inspect recent transactions) that help with this, but they vary by extension. Also, remember gasless illusions. While fees are low, transactions still require signatures and on-chain interactions. If a dApp promises "no gas," check what it's asking your wallet to sign—sometimes it’s approving large token allowances. That's a common surface for scams. Keep approvals granular and revoke allowances you no longer need. Solana Pay: bridging commerce and on-chain receipts Solana Pay is a simple but powerful primitive. It maps merchant invoices to on-chain payments and offers a web-native checkout that can be verified cryptographically. For artists selling NFTs or small merchants accepting crypto, that means a cleaner flow than manual transfers and screenshots. It can replace clunky payment instructions with a single signed transaction. That doesn't mean adoption is universal. Many merchants still prefer fiat rails or custodial solutions for settlement speed and chargeback handling. Yet for Web3-native shops (digital goods, limited drops, secondary market P2P trades), Solana Pay reduces friction and keeps receipts on-chain—valuable for provenance and royalties. Initially I assumed Solana Pay would be niche. But then I saw use cases—tips, instant merch drops, NFT raffles—where it made sense. Not everything should be on-chain, though. For recurring subscriptions or normalized refunds, hybrid solutions are still necessary (off-chain logic with on-chain settlement when needed). Practical tips for users in the Solana NFT + DeFi loop 1) Use a dedicated browser wallet for day-to-day activity and a separate cold storage for long-term holdings. 2) Keep approvals small and revoke them regularly. 3) Check marketplace metadata and contract addresses if you care about authenticity. 4) For payments, weigh Solana Pay's convenience against your need for merchant protections. I'll be honest: fiddly token accounts and occasional explorer outages still bug me. But the overall experience has matured. If you're new, start small. Buy a modest-priced NFT, try a simple swap, and watch how your chosen wallet surfaces data (token balance, recent transactions, NFTs). That gives you a baseline for what "normal" looks like in your client. FAQs Do I need a browser extension wallet for Solana NFTs? Short answer: yes for convenience. Browser extension wallets streamline signatures and integrate with marketplaces. They're the quickest path to minting and trading. If you're only viewing, you can use wallet-less viewers, but buying and signing require a wallet. Is Solana Pay safe for merchants? Solana Pay is cryptographically sound for payments, but merchants should pair it with off-chain reconciliation and fraud rules. For one-off digital goods it's great; for complex refunds or disputes you need hybrid processes. How do I avoid scams when buying NFTs? Verify contract addresses, check metadata sources, restrict approvals, and use wallets that show full transaction details before signing. If a deal looks too good or the site pushes urgent prompts, pause—breath—and inspect. Somethin' as simple as that often saves headaches. مطالعه
دستهبندی نشده Why Your Solana Wallet Extension Might Be Hiding the Full Story Whoa, this is surprising. I started tracking my Solana holdings and noticed weird gaps in history. At first I shrugged it off as UI lag. But as I dug deeper into transaction logs, staking rewards, and third-party explorers I saw patterns that didn't match what the wallet displayed, which made me dig even more and ask better questions. Here's what bugs me about portfolio views right now. Seriously, this is annoying. Initially I thought it was just a refresh issue on my browser extension. Actually, wait—let me rephrase that, it began as a refresh glitch then looked worse. On one hand the extension caches state to save bandwidth and speed, though actually when cache invalidation fails it can produce misleading balances and truncated histories that confuse casual users and professionals alike. My instinct said check settings, then check ledger exports. Hmm... somethin' feels off. I used a popular browser extension plus a desktop wallet and compared transaction histories. The extension showed pending swaps and failed transactions differently than the node logs did. If you're tracking tax lots or trying to reconcile staking yields for a quarterly report those differences matter a lot, especially when DeFi programs add program-derived-account interactions that the extension might simplify away. Okay, so check this out—there's a choice to make about trust and convenience. Where extensions fail — and a practical wallet pick Here's the thing. You can use a heavy full-node client and verify every signature manually. Or you can use a slick browser extension for speed and UX. On Solana, where block times are fast and program interactions are compact but complex, that UX trade-off sometimes strips contextual metadata from a transaction presentation, which is why tools that do deeper parsing become valuable for serious portfolio tracking. One wallet I like because of that balance (I've used it while staking at validators and interacting with Serum-style DEXs) is solflare, which offers both an extension and exportable transaction history. FAQ How should I reconcile extension data with on-chain logs? Whoa, timeline matters. That said, browser extensions can still be great if they expose exportable, auditable records. Make it a habit to export CSVs regularly and compare to raw node logs. If you're preparing records for taxes or audits, reconcile memo fields, stake accounts, validator commissions, and any program-derived-account transfers in a reproducible spreadsheet that you can share with an accountant if needed, because guesswork multiplies problems later. I'm not 100% sure about every edge case, but this workflow saved me time and headaches. مطالعه
دستهبندی نشده Cold, quiet, and locked: why I trust hardware wallets for serious crypto security Whoa, this is serious. I caught myself double-checking my seed phrase last night. Not just nervous like everyone else, but a real jolt of anxiety. Initially I thought a password manager would close the gap, but then realized hardware-level isolation actually prevents many remote compromises that software alone cannot reliably stop. That realization changed how I store digital value and access keys. Really, who knew? Hardware wallets feel fiddly at first for most people. They are cold, physical devices that insist on being separate from your computer. On one hand the friction is annoying, though actually that friction is what defends against phishing, keyloggers, and many social-engineering tactics that prey on human haste. So you trade immediate convenience for a layer of real security and peace. Hmm, my gut said something. My instinct said get a hardware wallet years ago. I put it off because setting up cold storage seemed time-consuming. Actually, wait—let me rephrase that: I delayed buying one because the perceived hassle outweighed the vague fear of losing funds until a close call made the choice obvious. The close call was a near-phishing event targeting an exchange account. Whoa, that was close. I almost clicked a link and gave up a 2FA token. Thankfully, the hardware wallet was offline and untouched by the scam. That incident made me map attack vectors in my head: hot wallet compromises, browser-based clipboard attacks, supply-chain tampering, and the forgotten backup at my kitchen drawer that anyone could find, somethin' embarrassing. I cleaned up bad habits and hardened all my access points quickly. Seriously, that simple? Here's the thing about hardware wallets: they isolate private keys in a secure chip. Even with a compromised computer, the signer stays offline and signs transactions without exposing keys. That architecture fundamentally reduces attack surface, though of course no solution is perfect and physical security, firmware updates, and supply provenance remain critical layers to manage. I'm biased, but I prefer hardware wallets for long-term holdings. Choosing wisely — what I looked for and why I started prioritizing open firmware, auditable bootloaders, and a transparent supply chain because those criteria actually matter when you have meaningful funds. I dug into vendor histories, read third-party audits, and even reached out to support teams in Silicon Valley and beyond to test response times and tone. Initially I thought that brand alone was enough, but then realized ecosystem compatibility, recovery options, and a vendor's track record with firmware patches were often the deciding factors for long-term trust. So I started testing devices, reading audit reports, and asking engineers very very hard questions. If you want to consult a manufacturer's docs during your research, check the trezor official for a straightforward place to begin. Okay, so check this out—there are three practical habits I recommend. First, never type your seed into a connected device; write it down on a durable medium and protect that backup physically, not just digitally. Second, keep small, hot balances for daily use and move the rest to cold storage; that split model reduces pressure and temptation. Third, test your recovery process on a clean device before you actually need it, because in a crisis you don't want surprises. I'm not 100% sure this is foolproof, but these steps have reduced my sleepless nights. On the nuance side, beware of supply-chain risks. Buying from an authorized retailer matters. (Oh, and by the way, avoiding sketchy third-party sellers is common-sense, but people still do it.) Tamper-evident packaging and verifying device fingerprints during setup are small chores that pay off later. And yes—physical theft is still a thing; a locked safe and good habits beat bravado any day. FAQ — quick answers to the questions I get most Do I need a hardware wallet if I only have a small amount of crypto? Short answer: maybe. If it's money you'd really miss, use a hardware wallet. If it's loose change and you're actively trading, a well-secured exchange or a software wallet with strong 2FA might be fine, though the risk profile differs. What about backups — how many, and where? Two backups in separate locations is a pragmatic start. Use durable media (metal if you can) for at least one copy, and avoid storing both backups in the same place or with the same person. I keep one offsite and one in a safe at home; your mileage may vary. Are all hardware wallets the same? No. They differ in UI, supported coins, open-source status, and security model. Read audits, check update policies, and consider community trust. Also, try the device yourself—if the UX frustrates you, you might opt for risky shortcuts later... مطالعه
دستهبندی نشده How I Lock Down a Crypto Portfolio: Practical Security, Passphrases, and Mistakes I Keep Making Whoa! I still remember the first time I nearly lost a small stash to a sloppy backup—my gut dropped, and I swore I'd never be careless again. That knee-jerk fear changed how I think about custodial risk, and eventually it shaped a routine that's simple enough to keep. At first I thought a single hardware wallet was all the armor I needed, but then I realized that human behavior is the weak link more often than the device. Initially I thought redundancy was overkill, but then reality taught me that one copy of paper in a drawer is a very very bad plan. Hmm... somethin' about repeated, small frictions (like the temptation to export keys to a laptop) compounds until an incident happens. Here's the thing. Security isn't glamorous. It is tedious, repetitive, and requires boring routines done well. Really? Yes. You can have the latest chain analytics and multisig schemes, but if you write your passphrase on a Post-it that's visible from the street, nothing else matters. My instinct said: "Use hardware wallets and be done." But actually, wait—let me rephrase that: hardware wallets are foundational, not magical. On one hand they protect private keys from malware; on the other, they depend on you to guard recovery material and to choose good passphrases and workflows. Portfolio management and security overlap more than most folks admit. Managing assets means knowing which holdings are long-term cold storage, which are active trading funds, and which require multisig or custodial services. I split funds into tiers—spend, trade, store—and treat each tier differently. The spend tier is small; it lives on a hot wallet with tight limits. The trade tier sits on an exchange or a hot wallet for convenience. The store tier is offline and lives on devices I can trust. Deciding those thresholds is personal, though—I'm biased toward cold storage because I value control over convenience. That preference bugs me sometimes when I want to move fast, but I'd rather sacrifice a little speed than risk a major loss. How I Use Hardware Wallets and Why I Recommend trezor suite When I set up hardware wallets I do it slowly and deliberately, verifying every step and mentally narrating the process so mistakes stand out later. I use multiple devices to avoid single points of failure and to test recovery procedures live (yes, in a dry run). For device management I prefer using the trezor suite on an air-gapped machine when possible, because its workflow encourages verification and displays important details clearly. That said, software is only part of the story—your backup strategy is the other half and often the one that breaks. Passphrases deserve special attention. A passphrase (sometimes called the 25th word) transforms a seed into countless possible wallets. Wow! Use it to add plausible deniability or to separate accounts, but treat it like a separate private key: don't store it with your seed and don't reuse it across multiple contexts. My rule is simple—unique passphrases per high-value account and a pattern that only I can reconstruct from memory cues. On the other hand, creating a passphrase too obscure or too long is risky if you can't reliably reproduce it under stress. I'm not 100% sure of the perfect balance, but practice and dry runs help immensely. There are three pragmatic techniques I use and recommend. First, test your recovery. Twice. Once immediately after setup and once from cold storage months later—preferably on a different device and location. Second, split backups geographically and by medium—steel plate for fireproofing at one location, a sealed envelope with a handwritten mnemonic at a second, and an encrypted digital backup in a secure vault only for the most disciplined. Third, for ultra-high-value positions, consider multisig across different vendors and jurisdictions. Multisig increases complexity, though actually it reduces systemic single points of failure—trade-offs everywhere. Portfolio visibility is part of security too. I track balances and exposure with read-only tools; I do not give any app private-key access unless necessary. Something felt off about apps requesting full access to wallets without clear reasoning—my instinct said no, and that has saved me from a few phishing traps. On the other hand, be careful: read-only API keys can leak information about holdings. On one hand this helps monitoring; on the other hand it creates privacy leaks that can attract targeted attacks. So I compartmentalize: different trackers for different accounts, and I avoid linking my main identity to large, long-term holdings. Threat modeling is underrated. Seriously? Yes—write down scenarios: lost device, stolen seed, social engineering, coercion, malware on a trading machine. For each scenario I map an action plan: who to contact, which keys to freeze, how to move funds across tiers. That exercise exposed a glaring issue in my own setup—too much reliance on a single recovery phrase. I corrected that by introducing an extra passphrase layer and by training a trusted ally in the dry-run process (and no, I won't say who). Operational security habits that I follow: use dedicated machines for signing when possible; keep OS and firmware up-to-date but test new updates first; prefer hardware wallets with verified open-source stacks (though open-source isn't a cure-all); and never export private keys unless you're doing controlled recovery. Tangent—oh, and by the way, I keep a simple physical checklist near my backup storage because when panic hits, you forget steps. Little things like that have prevented more messes than you'd imagine. Common mistakes I still catch myself making: mixing mnemonic backups with passphrase hints in the same location; procrastinating recovery tests; using obvious passphrases tied to public info; and over-centralizing keys. Double words and sloppy documentation sneak in—like writing the same note twice in different places because I'm anxious. These are human flaws. On one hand technology gives us tools; on the other, our behavior shapes how safe we actually are. FAQ How strong should a passphrase be? Make it unique and memorable to you without being guessable from public info. Aim for length over complexity, use unrelated words or a private phrase pattern, and practice recollection under stress. Do not store passphrases with your seed. Is multisig worth the hassle? For large portfolios, yes—multisig reduces single points of failure and distributes trust. For small balances the complexity may not be worth it. Evaluate your tolerance for operational complexity versus risk. What backup mediums are best? Steel plates for disasters, paper for quick access (but in a secure place), and encrypted digital backups only if you can manage keys without exposing them. Test restoration from each medium at least twice. مطالعه
دستهبندی نشده Why Monero Feels Different: Untraceable Transactions and Real Privacy Whoa, this surprised me. I remember the first time I sent XMR and felt a real wash of relief — like closing a door on a noisy porch. Monero's privacy isn't just checkbox privacy; it's operational privacy that changes the way you think about value transfer in public networks. I'm biased, but privacy matters to me in the same way seatbelts do: you hope you never need them, but you sure feel better wearing one. Initially I thought privacy coins were niche, then I realized they were foundational to how money should behave in a free society. Really? Yes, really. Okay, so check this out—monero's design choices are oriented toward default privacy; there are no optional knobs you must enable and forget. On one hand that simplicity is a huge win for everyday users, though actually, wait—let me rephrase that: the defaults make practical privacy accessible, but they also require users to trust that the tech works as advertised. My instinct said "solid," but then I dug into ring signatures, stealth addresses, and confidential transactions to see how the sausage is made. Here's the thing. The moment you stop treating every transaction like a public announcement, your mental model of money shifts. Transactions that once felt obvious become hidden in plain sight, and that changes behavior. At first glance the math looks like obfuscation for obfuscation's sake, but the underlying choices—decoupling sender and receiver, obscuring amounts—are deliberate protections against profiling, chain analysis, and casual snooping. Hmm...somethin' about that feels honest. The protocol uses ring signatures to mix outputs, which reduces linkability. Seriously? Yes. The cryptography blends plausible deniability with real-world usability, and that tradeoff is rare. On a technical level, that means you can't reliably say "these two transactions are from the same wallet" with any high degree of confidence—unless the user screws up or leaks metadata off-chain. How Monero Makes Transactions Untraceable Whoa, short version first. Ring signatures, stealth addresses, and RingCT (Ring Confidential Transactions) work together to hide participants and amounts. Medium summary: ring signatures mix a real input with decoys so observers can only guess which one is real, stealth addresses generate one-time public keys for each payment so receivers aren't tied to a single address, and RingCT hides the transferred amount while preserving balance math. On a deeper level the design resists deterministic heuristics used by chain analysis firms. Initially I thought "chain analysis has us beat," but then realized Monero's primitives intentionally break those heuristics—so tools that work on transparent chains are often useless here. Actually, wait—let me rephrase that: forensic companies can still do impressive work, but their approaches need different data sources and much more uncertainty when dealing with privacy-preserving outputs. Here's what bugs me about mainstream crypto narratives: people talk about privacy like it's a binary light switch—on or off. That framing is unhelpful. Privacy is a spectrum, and Monero deliberately shifts the default toward being private by design. The cumulative effect is behavioral: fewer accidental leaks, fewer patterns to exploit, and a lower baseline of exposure for users who don't obsess about OPSEC. Hmm, let me be practical. In my daily use, I treat Monero like cash. Hmm... I'm not 100% perfect here, but I try. If you send XMR to a vendor, their receipt doesn't fossilize a buyer's identity on a public ledger for posterity. That matters in many cases—political donations, personal safety, salary privacy, vendor discretion. Those are all mundane things, yet the consequences of exposure can be severe. Whoa—this part gets messy. Privacy isn't only about tech; it's also about metadata and human behavior. You can use perfect cryptography and still leak your identity through timing patterns, IP addresses, or reused touchpoints. On the other hand, Monero reduces the surface area that adversaries can exploit on-chain, and that's a real advantage if you pair it with decent operational practices. Seriously? Yup. A very important step is using a good wallet that prioritizes privacy norms. If you run a remote node or use a trusted remote node, that choice affects your network-level privacy. The easiest path for most people is a wallet that handles complexities for you, reducing mistakes and accidental exposures. For a straightforward, privacy-friendly option, try the monero wallet I keep recommending; I like how it balances usability with safe defaults. Whoa, small aside—I'm biased toward simple UX. This part bugs me: many privacy tools scare average users away with jargon. If Monero is to matter beyond enthusiasts, the UX needs to be friendly. On the flip side, some UX shortcuts can degrade privacy, so there's an ongoing tradeoff. Designers and engineers keep iterating to find that sweet spot between "secure" and "usable." Okay, so check this out—opponents will say "privacy coins enable bad actors." Hmm. My gut reaction is mixed. On one hand, bad actors do use privacy tools; though actually, wait—let me rephrase that: the same privacy that can be misused also protects ordinary people from predation, extortion, and surveillance. The ethical argument isn't settled by anecdotes; it's a policy question about balancing rights and risks. On a technical note, regulatory pressure has pushed exchanges and service providers to treat privacy coins differently. That has real implications for liquidity and onboarding. Initially I thought regulation would stifle privacy tech entirely, but then I realized that decentralized adoption and sovereign use-cases often continue regardless—users find ways to access tools they need. Still, the ecosystem adapts and sometimes suffers short-term friction. Here's the thing about anonymity sets. Bigger is better. The protective value of ring signatures increases as more outputs exist to hide among. That makes network adoption and consistent use important; if only a tiny group uses privacy-preserving features, their safety is weaker. So adoption is not merely vanity metrics—it's a material security property. Whoa, another human note: wallets matter. Bad wallet UX or careless custodial services can leak info that nullifies cryptographic protections. I'm guilty of rushing once and posting a transaction screenshot that revealed a balance. Really poor OPSEC on my end. You can do everything right on-chain and still reveal yourself by habit, so education and tooling are both crucial. Hmm, practical ops guide in a few lines. Use privacy-respecting wallets, avoid posting raw transaction screenshots, run your own node if you can, and mix times of sending funds across days rather than all at once. These are simple, and they add up. I'm not a preachy doomsayer, but I do care about making this accessible for people who just want to use money privately. Whoa—let's talk about tradeoffs. Privacy comes at cost: larger transactions, slightly heavier verification, and a smaller ecosystem of on-ramps. For many use-cases these costs are minor compared to the benefit. On the other hand, certain low-friction services still lag until liquidity grows. That doesn't mean the tech is broken—just that adoption and infrastructure evolve slower than ideal. Here's what excites me: ongoing research continually improves efficiency and privacy guarantees. Bulletproofs shrunk transaction sizes. Ongoing protocol upgrades refine ring signature algorithms and consensus adjustments. Initially I assumed you'd reach a ceiling, but the field keeps surprising me with clever optimizations that reduce costs while maintaining protections. Hmm... there's also the social layer. Community norms around sharing addresses, fundraising, and merchant adoption shape privacy effectiveness. The more people treat privacy as normal, the better everyone is protected. I'm not 100% sure how fast cultural shifts happen, but small habits compound—very very important to remember that. Whoa—before you go, a quick practical thought. If you want to try Monero, pick a wallet that balances usability and privacy defaults right away. Try small amounts, test receipts, and don't be afraid to ask community folks for setup tips (many are friendly, not all, but most). And remember: even a modest move to privacy can reduce your exposure significantly. FAQ Are Monero transactions truly untraceable? No single system is perfect, but Monero significantly reduces traceability compared to transparent ledgers. The combination of ring signatures, stealth addresses, and RingCT means observers face meaningful uncertainty. Operational mistakes or metadata leaks can still undermine privacy, so good practices are necessary. Will using Monero get me in legal trouble? I'm not a lawyer, but privacy tech is legal in many places. Regulatory landscapes vary and can change. Using privacy tools for lawful purposes is generally permissible; misuse of any money system can have legal consequences. Stay informed and consider local rules. How do I get started safely? Start with a user-friendly, privacy-focused wallet, test with small amounts, and slowly get comfortable. Running your own node is best for network privacy but not strictly required. For an accessible option that keeps privacy as a priority, try the monero wallet—I mention it because I like its defaults and it nudges users toward safer habits. مطالعه